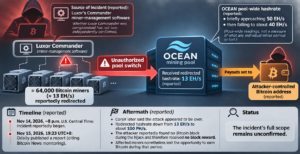
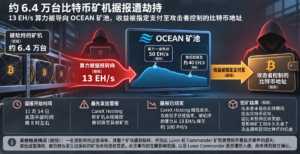
What happens when a mining fleet is switched to another pool without authorization? In a report published on November 15, 2026, at 22:17 Beijing time, BlockBeats said roughly 64,000 Bitcoin miners, representing about 13 EH/s, had their hashrate redirected to the OCEAN pool. The attackers reportedly set the payout address to a Bitcoin address they controlled.
The incident reportedly began around 20:00 US Central time on November 14 (10:00 Beijing time on November 15). OCEAN’s dashboard showed pool hashrate briefly approaching 50 EH/s before falling to about 40 EH/s. These are pool-wide readings, not a measure of any one operator’s hashrate.
Hosting provider CoreX Hosting first warned that some miners had been switched to other pools without authorization. One affected farm operator said its entire site had been hijacked and suggested Luxor’s Commander miner-management software as a possible source of the security incident. Other operators reported similar unauthorized pool switches days earlier, raising the possibility of a broader attack. Whether Commander was compromised has not been independently verified.
CoreX later said the attack appeared to have ended and that the redirected hashrate had fallen from 13 EH/s to about 100 PH/s. According to the report, the attackers mined no Bitcoin block during the hijack and therefore received no block reward. Affected miners nevertheless lost the opportunity to earn mining revenue during the time their hashrate was diverted; that mining time cannot be recovered. The incident’s full scope remains unverified.
Source: theblockbeats.info (originally published 2026-11-15 22:17 UTC+8)